Merkle Patricia tries in Ethereum: how state, proofs and eth_getProof work
How Ethereum's Merkle Patricia trie works: branch, extension and leaf nodes, the state, storage, transaction and receipt tries, and proofs with eth_getProof.
A Merkle Patricia trie (MPT) is the data structure Ethereum uses to commit to its state. It is a radix trie, so a key's hex digits spell out the path from the root to its value, and every node is referenced by the keccak256 hash of its contents, as in a Merkle tree. The result is one 32-byte root hash that fingerprints every account, balance and storage slot. Each block header carries that root, and anyone holding it can check a single value with a short proof instead of downloading the whole state.
This guide builds the MPT up from its two parents, walks through its three node types, shows the four tries Ethereum keeps, then verifies a real account and storage proof from eth_getProof in TypeScript.
Merkle trees and Patricia tries
The MPT combines two older ideas.
A Merkle tree hashes data in pairs up to a single root. Change any leaf and the root changes, so the root commits to all the data. To prove one leaf belongs, you hand over the sibling hashes on its path to the root: a proof whose size grows with the tree's depth, not with the number of leaves. Bitcoin uses a plain binary Merkle tree for the transactions in a block. It works well for a fixed list. It is awkward for data that is looked up and updated by key, like account balances.
A trie (from retrieval) stores key-value pairs by spelling the key out along the path. To find key a7f9, go to child a, then 7, then f, then 9. Keys that share a prefix share the path to it, and lookups, inserts and deletes cost one step per key character. A radix trie or Patricia trie (PATRICIA: Practical Algorithm To Retrieve Information Coded In Alphanumeric) compresses chains of single-child nodes into one node that stores the shared run of characters, so sparse keys don't create long empty paths.
Ethereum's version, which ethereum.org calls a modified Merkle Patricia trie, is a Patricia trie over hex digits (nibbles) where children are linked by hash. Two properties follow:
- One root for any set of contents. The same key-value pairs always build the same trie and the same root, whatever order they were inserted in. A plain Merkle tree over a list doesn't have that property.
- Cheap updates. Changing one value rewrites only the nodes on its path, so a new root after a block of changes costs a few hashes per touched key, not a rebuild.
The three node types: branch, extension and leaf
Every node is an RLP-encoded list. There are three kinds that hold data, plus the empty value:
| Node | Contents | What it does |
|---|---|---|
| Branch | 17 items: 16 child references and a value | Splits on the next nibble: item i points to the subtree for keys whose next nibble is i |
| Extension | [encodedPath, child] |
Skips a run of nibbles that every key below it shares, then points to one child (always a branch) |
| Leaf | [encodedPath, value] |
Holds the rest of one key's path and that key's value |
| Empty | the empty string | No child in that slot; the empty trie's root is 0x56e81f171bcc55a6ff8345e692c0f86e5b48e01b996cadc001622fb5e363b421 |
A branch's 17th item holds a value only when a key ends exactly at that branch. The state and storage tries use fixed-length keys (32-byte hashes), so no key can end part-way down the path and in those tries it is always empty.
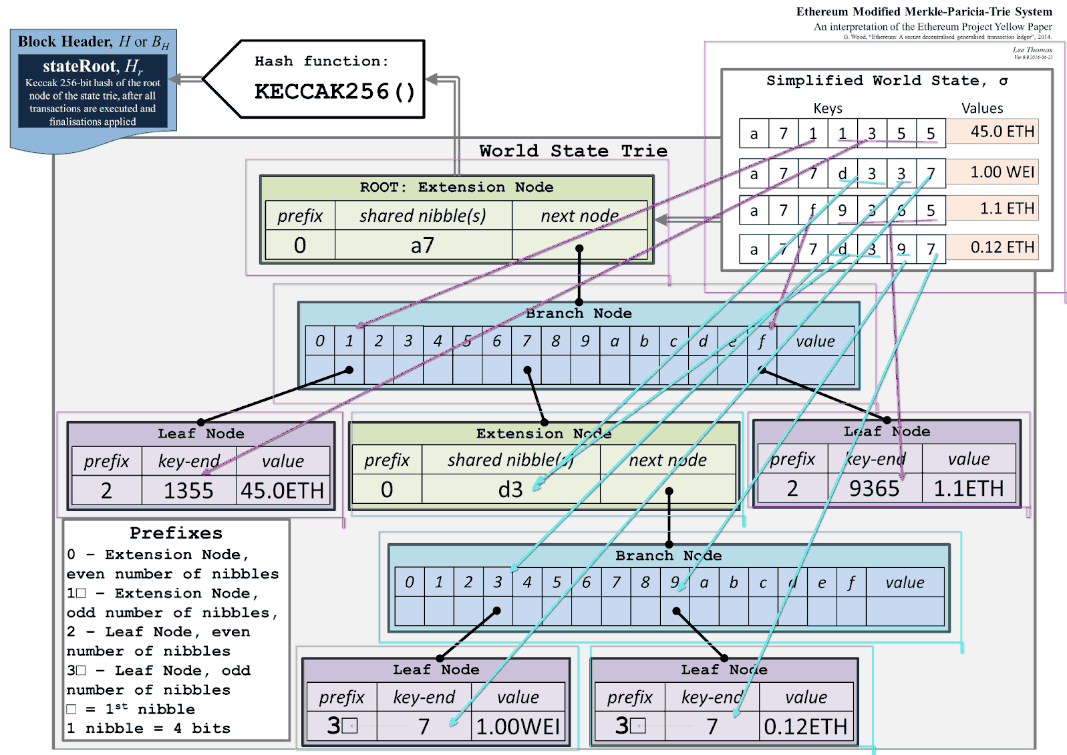
Hex-prefix encoding. Leaves and extensions both store a partial path, and a path can have an odd number of nibbles, so the path is packed with a one-nibble flag in front:
| First nibble | Node type | Path length |
|---|---|---|
0 |
Extension | Even (a padding 0 nibble follows) |
1 |
Extension | Odd |
2 |
Leaf | Even (a padding 0 nibble follows) |
3 |
Leaf | Odd |
Hash references. A parent points to a child by the keccak256 hash of the child's RLP encoding. If that encoding is shorter than 32 bytes, the child is embedded in the parent instead of hashed. The root is always referenced by its hash.
Here is the classic small example from ethereum.org, with four keys of seven nibbles each. Real Ethereum keys are 64 nibbles long; the shape is the same.
keys: a711355 a77d337 a7f9365 a77d397 root: extension "a7" (all four keys start with a7) └─ branch ├─ 1: leaf "1355" → a7 1 1355 = a711355 ├─ 7: extension "d3" (a77d337 and a77d397 share d3) │ └─ branch │ ├─ 3: leaf "7" → a7 7 d3 3 7 = a77d337 │ └─ 9: leaf "7" → a7 7 d3 9 7 = a77d397 └─ f: leaf "9365" → a7 f 9365 = a7f9365Change the value at a77d397 and only five nodes change: its leaf, the branch above it, the d3 extension, the first branch and the root extension, so the root hash changes too. Every other node, and its hash, stays as it was.
Keys and values: RLP and keccak256
Ethereum doesn't use raw keys as paths in its state and storage tries. It uses keccak256(key), which ethereum.org calls the "secure" trie. Hashing the key spreads entries evenly, so every path is 64 nibbles and the trie stays shallow and balanced, and nobody can craft addresses or slot numbers that build one very deep path to slow nodes down.
Values and nodes are serialised with RLP (recursive length prefix), Ethereum's encoding for nested byte arrays. Integers are big-endian with leading zero bytes stripped, so 0 encodes as the empty string.
The four tries in Ethereum
Ethereum keeps one state trie, one storage trie per contract, and a transaction trie and a receipt trie per block. Their roots are what tie the data to the chain:
| Trie | Key | Value | Root lives in |
|---|---|---|---|
| State | keccak256(address) |
RLP([nonce, balance, storageRoot, codeHash]) |
Block header, stateRoot |
| Storage | keccak256(slot) (32 bytes) |
RLP(value), the slot's value with leading zeros stripped |
The account's storageRoot |
| Transactions | RLP(index in block) |
The encoded transaction | Block header, transactionsRoot |
| Receipts | RLP(index in block) |
The encoded receipt: status, cumulative gas used, logs bloom, logs | Block header, receiptsRoot |
The state trie is the one that changes all the time: every block updates balances, nonces and storage, and the new stateRoot goes in the header. Each contract's storage trie hangs off its account through storageRoot, so a storage write changes the storage root, which changes the account leaf, which changes the state root. The Ethereum accounts guide covers the four account fields in more detail.
The transaction and receipt tries are built once per block and never change afterwards. Their keys are the position in the block, not a hash, because they are a list. Since the Shanghai upgrade a block header also carries a withdrawalsRoot, the root of a trie of validator withdrawals built the same way (EIP-4895).
eth_getBlockByNumber returns all of these roots with the header. The Yellow Paper (Appendix D) is the formal specification of the trie.
A worked example: walk a real account proof
Take the USDC token contract, 0xa0b86991c6218b36c1d19d4a2e9eb0ce3606eb48. Its key in the state trie is the keccak256 hash of its address:
keccak256(0xa0b86991c6218b36c1d19d4a2e9eb0ce3606eb48)= 0x7b5855bb92cd7f3f78137497df02f6ccb9badda93d9782e0f230c807ba728be0The path from the state root starts 7, b, 5, 8, … . At mainnet block 26465384 the proof for this account had nine nodes: eight branch nodes, taking child 7, then b, 5, 8, 5, 5, b, b, and then a leaf holding the remaining 56 nibbles and the account's value. The upper branches were full: 532 bytes each, 16 child hashes of 32 bytes plus RLP overhead. The whole account proof was 3,847 bytes, and each storage slot proof another eight nodes and 3,136 bytes. That is all it takes to prove one value against the root of the entire state.
No extension node appeared on this path. Because keys are hashes, they spread evenly, so near the top of a trie as large as Ethereum's state every branch is full, and paths only diverge into leaves near the bottom. Extensions turn up where a few keys share a long prefix below a branch, which is common in small tries and rare high in the state trie.
The next section fetches that proof and checks it.
Merkle proofs with eth_getProof
EIP-1186 added eth_getProof to the standard JSON-RPC API. Given an address, a list of storage slots and a block, it returns the account's fields, the account proof (the nodes from the state root to the account's leaf) and one proof per storage slot (the nodes from the account's storageRoot to the slot). GoldRush serves it on Ethereum mainnet through GoldRush JSON-RPC, authenticated with a bearer API key (authentication):
curl https://rpc.goldrushdata.com/v1/eth-mainnet \ -H "Authorization: Bearer $GOLDRUSH_API_KEY" \ -H "Content-Type: application/json" \ -d '{ "jsonrpc": "2.0", "id": 1, "method": "eth_getProof", "params": ["0xa0b86991c6218b36c1d19d4a2e9eb0ce3606eb48", ["0x0000000000000000000000000000000000000000000000000000000000000000"], "latest"] }'The response has address, balance, nonce, codeHash, storageHash (the account's storage root), accountProof (an array of RLP-encoded nodes, root first) and storageProof (one { key, value, proof } per slot). The eth_getProof method page lists the parameters.
A proof is only worth something if you check it against a root you trust. The code below takes the stateRoot from the block header (eth_getBlockByNumber), asks for a proof at that same block, and walks it node by node with viem's keccak256 and fromRlp. It checks that every node hashes to the reference its parent holds, follows the key's nibbles through branches and extensions, and compares the leaf with the fields the node returned. A proof that a key is absent ends at an empty branch slot or a path that diverges; the code returns null there, which for a storage slot means the value is zero.
import { fromRlp, keccak256, type Hex } from "viem"; const RPC_URL = "https://rpc.goldrushdata.com/v1/eth-mainnet"; async function rpc<T>(method: string, params: unknown[]): Promise<T> { const res = await fetch(RPC_URL, { method: "POST", headers: { Authorization: `Bearer ${process.env.GOLDRUSH_API_KEY}`, "Content-Type": "application/json", }, body: JSON.stringify({ jsonrpc: "2.0", id: 1, method, params }), }); const body = await res.json(); if (body.error) throw new Error(`${method}: ${body.error.message}`); return body.result as T;} type Item = Hex | Item[]; // a decoded RLP item: a byte string or a list const nibbles = (hex: Hex) => [...hex.slice(2)].map((c) => parseInt(c, 16));const toBigInt = (hex: Hex) => (hex === "0x" ? 0n : BigInt(hex)); // Leaf and extension nodes store their path in hex-prefix encoding: the first nibble says// leaf (2, 3) or extension (0, 1), and odd (1, 3) or even (0, 2) length.function decodePath(encoded: Hex) { const n = nibbles(encoded); return { isLeaf: n[0] >= 2, path: n[0] % 2 === 1 ? n.slice(1) : n.slice(2) };} // Walk a proof from the root hash down the path keccak256(key). Returns the RLP-encoded// value, or null when the proof shows the key is not in the trie.function verifyProof(root: Hex, key: Hex, proof: Hex[]): Hex | null { const path = nibbles(keccak256(key)); const nodes = new Map(proof.map((rlp) => [keccak256(rlp), rlp])); let ref: Item = root; let depth = 0; for (;;) { let node: Item[]; if (typeof ref === "string") { if (ref === "0x") return null; // empty child: the key is absent const rlp = nodes.get(ref); if (!rlp) throw new Error(`no node in the proof hashes to ${ref}`); node = fromRlp(rlp) as Item[]; } else { node = ref; // a node under 32 bytes is embedded in its parent, not hashed } if (node.length === 17) { console.log(` branch at nibble ${depth}: take child ${path[depth].toString(16)}`); ref = node[path[depth]]; depth += 1; continue; } const { isLeaf, path: part } = decodePath(node[0] as Hex); if (part.some((n, j) => path[depth + j] !== n)) return null; // path diverges: absent depth += part.length; if (isLeaf) { console.log(` leaf at nibble ${depth - part.length}: ${part.length} nibbles left`); return node[1] as Hex; } console.log(` extension at nibble ${depth - part.length}: skip ${part.length} shared nibbles`); ref = node[1]; }} type Proof = { balance: Hex; nonce: Hex; codeHash: Hex; storageHash: Hex; accountProof: Hex[]; storageProof: { key: Hex; value: Hex; proof: Hex[] }[];}; async function proveAccount(address: Hex, slots: Hex[]) { // Pin one block, so the proof and the root come from the same state. const block = await rpc<{ number: Hex; stateRoot: Hex }>("eth_getBlockByNumber", ["latest", false]); const proof = await rpc<Proof>("eth_getProof", [address, slots, block.number]); console.log(`account ${address} at block ${BigInt(block.number)}`); const account = verifyProof(block.stateRoot, address, proof.accountProof); if (!account) throw new Error("the proof says the account does not exist"); // An account leaf's value is RLP([nonce, balance, storageRoot, codeHash]). const [nonce, balance, storageRoot, codeHash] = fromRlp(account) as Hex[]; if (toBigInt(nonce) !== BigInt(proof.nonce)) throw new Error("nonce mismatch"); if (toBigInt(balance) !== BigInt(proof.balance)) throw new Error("balance mismatch"); if (storageRoot !== proof.storageHash || codeHash !== proof.codeHash) throw new Error("root mismatch"); console.log(`verified: nonce ${toBigInt(nonce)}, balance ${toBigInt(balance)} wei`); for (const slot of proof.storageProof) { console.log(`storage slot ${slot.key}`); const leaf = verifyProof(storageRoot, slot.key, slot.proof); const value = leaf ? toBigInt(fromRlp(leaf) as Hex) : 0n; // absent means zero if (value !== BigInt(slot.value)) throw new Error(`slot ${slot.key} mismatch`); console.log(`verified: 0x${value.toString(16)}`); }} await proveAccount("0xa0b86991c6218b36c1d19d4a2e9eb0ce3606eb48", [ "0x0000000000000000000000000000000000000000000000000000000000000000", "0x0000000000000000000000000000000000000000000000000000000000000001",]);Run against a response recorded at block 26465384, it printed this (the second slot's walk is cut):
account 0xa0b86991c6218b36c1d19d4a2e9eb0ce3606eb48 at block 26465384 branch at nibble 0: take child 7 branch at nibble 1: take child b branch at nibble 2: take child 5 branch at nibble 3: take child 8 branch at nibble 4: take child 5 branch at nibble 5: take child 5 branch at nibble 6: take child b branch at nibble 7: take child b leaf at nibble 8: 56 nibbles leftverified: nonce 1, balance 0 weistorage slot 0x0000000000000000000000000000000000000000000000000000000000000000 branch at nibble 0: take child 2 branch at nibble 1: take child 9 branch at nibble 2: take child 0 branch at nibble 3: take child d branch at nibble 4: take child e branch at nibble 5: take child c branch at nibble 6: take child d leaf at nibble 7: 57 nibbles leftverified: 0xfcb19e6a322b27c06842a71e8c725399f049ae3astorage slot 0x0000000000000000000000000000000000000000000000000000000000000001 ...verified: 0x4914f61d25e5c567143774b76edbf4d5109a8566Change one byte of any proof node, or the balance the node returned, and it throws. That is the point: the proof only has to be consistent with a stateRoot you already trust, such as one from a header your light client or consensus client has verified, and the RPC provider doesn't have to be trusted at all. Bridges, light clients and storage-proof protocols use exactly this check. For the account fields themselves, the plain eth_getBalance and eth_getStorageAt calls are simpler when you trust the node.
Why clients store flat state
The trie is how Ethereum commits to state. It isn't the fastest way to read it. Reading one account by walking the trie takes a database lookup per level, about nine on mainnet as the example shows, and every write rewrites a node per level on its path. So execution clients keep the state in a second, flat form, one key-value lookup per account or slot, and use the trie mainly to compute roots and serve proofs.
Geth keeps a flat snapshot beside its trie and, in its path-based scheme, stores trie nodes by position so updates overwrite in place. Erigon goes further and stores only flat state, computing the state root during execution rather than keeping the trie as the source of truth. The Erigon vs Geth guide compares the two designs, including which clients can serve eth_getProof for old blocks.
What may replace the Merkle Patricia trie
The MPT's proofs are large: a branch node carries 16 sibling hashes, so a single-account proof runs to a few kilobytes, as above. That matters for stateless clients, which would verify blocks using proofs shipped with them instead of a local copy of the state (ethereum.org on statelessness). Two proposals would change the state's structure for that reason:
- Verkle trees (EIP-6800): a wide tree whose nodes commit to their children with vector commitments instead of hashes, so a proof doesn't have to carry every sibling.
- A binary tree (EIP-7864): a unified binary trie, where a proof carries one sibling hash per level instead of up to fifteen, so proofs are smaller than the hexary MPT's.
Both are proposals, not scheduled upgrades. Today the state, transaction, receipt and withdrawal roots in every Ethereum block header are Merkle Patricia trie roots.
Frequently asked questions
What is the difference between a Merkle tree and a Merkle Patricia trie?
A Merkle tree hashes a list of items up to one root and proves that an item is in the list. A Merkle Patricia trie is a key-value map: the key spells out the path, nodes are linked by hash, and the same contents always give the same root. That makes it suited to state that is looked up and updated by key, like Ethereum's accounts and contract storage.
Is it a Merkle Patricia tree or trie?
Both names are used for the same thing. Ethereum's documentation says "trie", from retrieval, because it is a prefix tree that stores values along key paths. "Tree" is common in papers and older articles.
What are the node types in a Merkle Patricia trie?
Branch nodes (17 items: one child per hex digit plus a value), extension nodes (a shared run of nibbles and one child), and leaf nodes (the rest of a key's path and its value). Empty slots are the empty string. Leaves and extensions store their partial path in hex-prefix encoding, whose first nibble tells them apart.
What does the state root in a block header prove?
It is the root hash of the state trie after the block's transactions run, so it commits to every account's nonce, balance, code hash and storage root, and through each storage root to every contract storage slot. Any of those values can be checked against it with a Merkle proof from eth_getProof.
Can I get a Merkle proof for an old block?
eth_getProof takes a block number, but answering for an old block needs a node that still has that block's trie nodes. Many full nodes and providers only serve proofs for recent blocks; older blocks need an archive node that keeps historical trie data. Check the block range your provider supports for the method before relying on it.
Next steps
- Request a proof with eth_getProof on GoldRush JSON-RPC, and see the GoldRush JSON-RPC overview for endpoints and keys.
- Read balances, transactions and token data for any address with the GoldRush Ethereum API.
- Compare how Erigon and Geth store state.
- Learn what each Ethereum account stores.
- See how RPC nodes serve JSON-RPC calls like this one.
- Read the ethereum.org Merkle Patricia trie page for the full encoding rules.