How do ZK rollups work? Validity proofs, zkEVMs and data availability
A ZK rollup is a layer 2 that proves its transactions valid on Ethereum. How validity proofs, zkEVMs and data availability work, and ZK vs optimistic rollups.
A ZK rollup (zero-knowledge rollup) is a layer 2 blockchain that executes transactions off Ethereum, then posts the transaction data and a new state root to Ethereum together with a validity proof: a short cryptographic proof that the new state is the correct result of applying those transactions. A smart contract on Ethereum checks the proof, and only then accepts the new state. Ethereum never re-executes the rollup's transactions, but it never has to trust the rollup's operator either, because an invalid state transition can't produce a valid proof.
This guide covers why Ethereum needs layer 2s, how a ZK rollup batch moves from the sequencer to the verifier contract, SNARKs vs STARKs, the four zkEVM types, how ZK rollups compare with optimistic rollups, where rollups put their data, and how to watch a real batch go through the pipeline on zkSync Era.
Why Ethereum needs layer 2s
Every Ethereum node re-executes every transaction and stores the data behind every block, so throughput is capped by what an ordinary node can process. When demand exceeds that block space, users bid against each other and fees rise. This is the scalability trilemma: a blockchain can easily get two of decentralization, security and scalability, but raising throughput on the base layer usually means bigger, more expensive nodes and fewer people able to run them.
Ethereum's answer is to keep the base layer (layer 1, or L1) small and verifiable, and move execution to layer 2s (L2s). A rollup executes transactions on its own chain, then writes its data and results back to Ethereum, so that it inherits Ethereum's security: anyone can rebuild the rollup's state from what is on Ethereum, and Ethereum's contracts decide which state is final. Sidechains and validiums, by contrast, keep their data or their consensus elsewhere and depend on their own security. The two main rollup families differ in how Ethereum learns that a rollup's new state is correct: optimistic rollups assume it is unless someone proves fraud, and ZK rollups prove it every time.
This is why Ethereum is often described as modular: it acts as the settlement, consensus and data availability layer while rollups do most of the execution. The modular blockchain guide covers that split in detail.
How a ZK rollup works, step by step
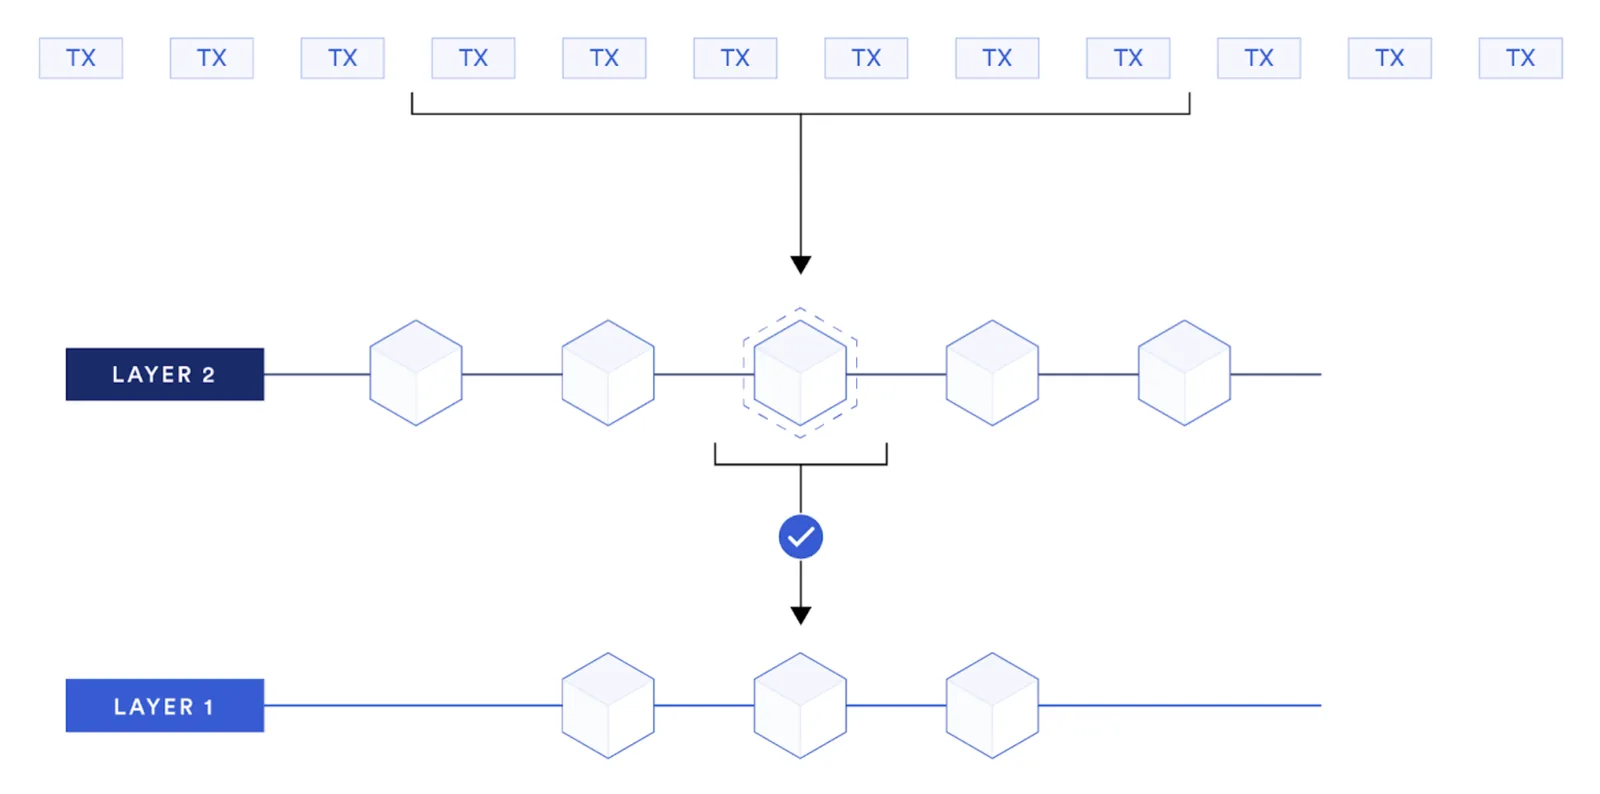
A ZK rollup has a few off-chain parts (a sequencer, a prover and the rollup's own nodes) and a few contracts on Ethereum (the rollup contract that stores state roots, a verifier contract, and a bridge). A batch of transactions goes through them in this order:
- Users send transactions to the sequencer. The sequencer orders them, executes them against the rollup's current state and gives users a fast "soft" confirmation. At this point nothing is final on Ethereum.
- The sequencer seals a batch. Many L2 blocks are grouped into one batch. Executing the batch produces a new state root, a Merkle root that commits to every account balance and contract storage slot on the rollup.
- The batch is committed to Ethereum. A transaction on L1 posts the batch's data (or a compressed form of it) and the new state root to the rollup contract. Since EIP-4844 the data usually goes into blobs; see where ZK rollups put their data.
- The prover generates a validity proof. Off-chain, specialised prover machines (often GPU clusters) build a proof that executing exactly this batch's transactions on the old state root gives the new state root. This is the expensive step, and the reason proofs can lag minutes or hours behind the batch.
- The verifier contract checks the proof on Ethereum. The proof, the old and new state roots and a commitment to the batch data are passed to the verifier contract. Checking a proof costs a roughly fixed amount of gas however many transactions the batch holds, which is where the scaling comes from. If the check passes, the contract records the new state root as proven.
- The batch is finalized. Once the state root is final on Ethereum, withdrawals in that batch can be completed: a user proves against the state root that their withdrawal is in it, and the bridge contract releases the funds on L1. Some rollups add a deliberate delay between proving and executing a batch as a safety margin.
Two more pieces matter for users. The bridge holds the assets deposited into the rollup, and is released only against proven state, so it can't be drained by a sequencer that lies about balances. And because a single sequencer could censor transactions, ZK rollups let users submit transactions directly to the L1 contract (a priority queue or forced-inclusion path) that the sequencer has to include. How decentralised the sequencer and prover are, and who can upgrade the contracts, varies by rollup and is exactly what L2 risk frameworks score.
Zero-knowledge proofs: SNARKs and STARKs
A zero-knowledge proof lets a prover convince a verifier that a statement is true without the verifier redoing the work, and optionally without revealing the private inputs. For scaling, the important property is succinctness: the proof is small and quick to check, however large the computation it covers. Despite the name, most ZK rollups publish all their transaction data and use proofs for succinctness, not privacy.
Two families of proof systems are used in production:
| zk-SNARKs | zk-STARKs | |
|---|---|---|
| Stands for | Succinct Non-interactive ARgument of Knowledge | Scalable Transparent ARgument of Knowledge |
| Proof size | Small (hundreds of bytes for common schemes) | Larger (tens to hundreds of kilobytes) |
| Cost to verify on Ethereum | Low | Higher, because the proof is bigger |
| Trusted setup | Many schemes need one: per circuit (Groth16) or one universal ceremony (PLONK-style with KZG) | None: transparent, built on hash functions |
| Cryptographic assumptions | Elliptic-curve pairings, not quantum-resistant | Hash functions, believed to be quantum-resistant |
| Prover speed | Slower for very large computations | Fast for large computations |
A trusted setup generates public parameters from secret randomness that has to be destroyed; if every participant in the setup ceremony colluded, they could forge proofs. Multi-party ceremonies with many participants make that unlikely, since one honest participant is enough.
In practice many rollups combine the two. They prove a batch with a STARK-style system, which is fast and transparent, then prove the STARK verifier itself inside a small SNARK so that the proof Ethereum checks is cheap. The same idea, recursion, lets a prover split a huge batch into pieces, prove each in parallel and aggregate the proofs into one.
What is a zkEVM? Types 1 to 4
A zkEVM is a ZK rollup whose virtual machine runs Ethereum smart contracts, so developers can deploy Solidity contracts and use Ethereum tooling. Proving the EVM is hard, because it was not designed with proofs in mind (its Keccak hashing and Merkle Patricia state tree are expensive to prove). zkEVMs therefore trade some compatibility for prover speed. Vitalik Buterin's 2022 classification of zkEVMs is the usual vocabulary:
- Type 1: fully Ethereum-equivalent. Changes nothing about Ethereum, including its state tree and hashing, so it could prove Ethereum L1 blocks themselves. Most compatible, slowest to prove. Taiko describes itself as a Type 1 zkEVM.
- Type 2: fully EVM-equivalent. Runs EVM bytecode unchanged but swaps some internals, such as the state tree or hash function, for proof-friendly ones. Existing contracts and tools work; tools that read Ethereum's state structure directly may not. Linea and Scroll target this level.
- Type 3: almost EVM-equivalent. Drops or changes a few hard-to-prove features, such as some precompiles, so most but not all contracts work unchanged. Several zkEVMs launched as Type 3 on their way to Type 2.
- Type 4: high-level-language equivalent. Compiles Solidity or Vyper source to a different, proof-friendly VM. Fastest to prove, but bytecode-level behaviour (contract addresses, some opcodes, debugging tools) can differ. zkSync Era started here with its own EraVM and has since added an EVM bytecode emulator.
Starknet is a ZK rollup that isn't a zkEVM at all: it runs the Cairo VM and contracts are written in Cairo, a language designed for STARK proofs.
ZK rollups vs optimistic rollups
Both kinds of rollup execute off-chain and post their data to Ethereum. The difference is how Ethereum is convinced that a new state root is correct.
| ZK rollups | Optimistic rollups | |
|---|---|---|
| How a state root is accepted | A validity proof is verified on Ethereum before the root is final | The root is assumed valid; anyone can challenge it with a fraud (fault) proof during a challenge window |
| Withdrawal to Ethereum | Once the batch is proven and executed, which can be hours, with no challenge window | After the challenge window, typically about seven days (bridges and liquidity providers offer faster exits for a fee) |
| Security assumption | The proof system and verifier contract are sound | At least one honest party is watching and will challenge an invalid root |
| Running cost | Proof generation needs heavy computation | No proving; challenges are rare |
| EVM compatibility | Varies by zkEVM type (above), and has improved quickly | EVM-equivalent from the start |
| Examples | zkSync Era, Starknet, Linea, Scroll, Taiko | Arbitrum One, OP Mainnet, Base |
Optimistic rollups were first to market with full EVM compatibility, which is why many of the largest L2s are optimistic. ZK rollups give faster, proof-backed exits and don't depend on someone watching for fraud. Some optimistic stacks are adding ZK proofs, and the line between the two is blurring.
Where ZK rollups put their data
A validity proof shows that the new state is correct, but it doesn't tell anyone what the state is. To check their balance, build the next block or leave the rollup without the operator's help, users need the data behind each batch. If an operator published a proof but withheld the data (a data withholding attack), funds would be safe from theft but could be frozen, because nobody else could reconstruct the state to prove a withdrawal. Data availability (DA) is the guarantee that this data was published and can be downloaded. It is also the largest part of most rollups' costs, so where the data goes is the main design choice after the proof system.
- Rollup: data on Ethereum. The original design posted batch data as transaction calldata, which is permanent but expensive. Since the Dencun upgrade activated EIP-4844 in March 2024, rollups post data in blobs: large data attachments with their own fee market, much cheaper than calldata, that consensus nodes keep for about 18 days. That is long enough for anyone to download and archive the data, and the verifier checks the proof against the blob's commitment. Ethereum is scaling blob capacity with PeerDAS, which lets nodes sample blob data instead of downloading all of it; the PeerDAS guide explains how.
- Validium: data with a committee. The data stays off Ethereum, held by a data availability committee (DAC) of known parties that sign that they have it. Much cheaper, but users rely on the committee not to withhold data: if it does, the state can be proven correct yet frozen. A validium is not a rollup in the strict sense.
- Volition: the user chooses. A hybrid where each account or transaction chooses rollup mode (data on Ethereum) or validium mode (data off-chain), trading cost against security per use. StarkWare's StarkEx offered this mode.
- External DA layers. Instead of a committee, the data goes to a blockchain built for data availability, such as Celestia, Avail or EigenDA, which use data availability sampling or their own operator sets to attest that the data was published. Security then depends on that layer as well as Ethereum, and L2 risk trackers classify these chains separately from rollups.
Rollups also cut how much data they post. Some publish state diffs (the storage slots that changed in a batch, with their final values) instead of every transaction, so a slot written a hundred times in one batch costs one entry; zkSync Era and Starknet work this way. Others publish transactions but compress each batch before posting it. Both lower the data cost per transaction, at the price of making it harder to reconstruct individual transactions from L1 data alone.
Watch a zkSync Era batch move through Ethereum
zkSync Era's nodes expose its batch pipeline through extra zks_ JSON-RPC methods, so you can watch the steps above happen. This script asks zkSync Era's public RPC endpoint for the latest batch number, then for the details of an older batch and a recent one: how many transactions each holds, its state root, and the Ethereum transactions that committed, proved and executed it.
// batches.mjs. Node 18+ (built-in fetch). No API key: zkSync Era's public RPC endpoint.const RPC = "https://mainnet.era.zksync.io"; async function rpc(method, params = []) { const res = await fetch(RPC, { method: "POST", headers: { "Content-Type": "application/json" }, body: JSON.stringify({ jsonrpc: "2.0", id: 1, method, params }), }); const { result, error } = await res.json(); if (error) throw new Error(`${method}: ${error.message}`); return result;} async function batchLifecycle(number) { const b = await rpc("zks_getL1BatchDetails", [number]); console.log(`Batch ${b.number}: ${b.l2TxCount} L2 txs, ${b.l1TxCount} L1 txs, status ${b.status}`); console.log(` state root ${b.rootHash}`); console.log(` committed ${b.committedAt ?? "not yet"} ${b.commitTxHash ?? ""}`); console.log(` proven ${b.provenAt ?? "not yet"} ${b.proveTxHash ?? ""}`); console.log(` executed ${b.executedAt ?? "not yet"} ${b.executeTxHash ?? ""}`);} const latest = Number(await rpc("zks_L1BatchNumber"));await batchLifecycle(latest - 1000); // an older batch: committed, proven and executed on Ethereumawait batchLifecycle(latest - 5); // a recent one: still moving through the pipelineRun with node batches.mjs. On 21 November 2026 it printed:
Batch 519504: 147 L2 txs, 1 L1 txs, status verified state root 0xbf8e3135427a0baedf518848bbd7d834fec3c3814eba347a273946493bcab95f committed 2026-10-31T21:49:49.568847Z 0x85b9970f65f28a223e7f2aec29f5cb2425a37f66cb92e154728c224dc7d2f2a2 proven 2026-10-31T22:59:55.856485Z 0x6aad531b59ea7c4348948de18112c3a10883129ca6dc93c99742c2fbf4d718b1 executed 2026-11-01T22:08:33.237577Z 0x74971a97b3fa92ce7e29f7fb4b327abc51dcb8b30a58c962a155cf730c9c4353Batch 520499: 396 L2 txs, 1 L1 txs, status sealed state root 0x82b14ad9e3839bb7e8e14ce91f1078094468884fca93f8effb9d49421fb18891 committed 2026-11-21T16:04:02.907715Z 0x90ddb62d8ea026da74e19ff630a3e79f46c4c3f178ea90bbe44e856d49954204 proven 2026-11-21T16:48:42.092851Z 0x1301d267957ece211e208014733e1640209a8b34a78138412b72e19e4e9ba540 executed not yetEach hash is an Ethereum mainnet transaction you can open in a block explorer: the commit posts the batch's data and state root, the prove transaction runs the verifier contract, and the execute transaction finalizes the batch. In this run the proof landed roughly an hour after the commit, and execution about a day after the proof: zkSync Era holds proven batches for a while before executing them, as a safety margin. l1TxCount counts transactions submitted through the Ethereum contract (the priority queue), the path users can take if the sequencer ignores them. Other ZK rollups expose the same lifecycle through their own contracts and APIs; the method names here are zkSync-specific (see the zks_ RPC reference).
Reading data from ZK rollups
For an app, a zkEVM chain looks like any EVM chain: blocks, transactions, logs and balances, behind a JSON-RPC endpoint. The work starts when you support several rollups at once, each with its own endpoint, token list and quirks. GoldRush indexes ZK rollups including zkSync Era, Linea, Scroll and Taiko, in the same response format as Ethereum and the optimistic rollups.
The GoldRush wallet balance API returns one address's native and token balances, with USD quotes, across several EVM chains in one call, so one request covers an address's holdings on every ZK rollup you care about. It costs 2.5 credits for the first page of results:
// Node 18+ (built-in fetch). Set GOLDRUSH_API_KEY in your environment.const API_KEY = process.env.GOLDRUSH_API_KEY; // ZK rollups that settle on Ethereum.const ZK_ROLLUPS = ["zksync-mainnet", "linea-mainnet", "scroll-mainnet", "taiko-mainnet"]; async function zkRollupHoldings(address) { const url = new URL(`https://api.covalenthq.com/v1/allchains/address/${address}/balances/`); url.searchParams.set("chains", ZK_ROLLUPS.join(",")); url.searchParams.set("quote-currency", "USD"); const res = await fetch(url, { headers: { Authorization: `Bearer ${API_KEY}` } }); if (!res.ok) throw new Error(`GoldRush returned HTTP ${res.status}`); const { data } = await res.json(); const byChain = {}; for (const item of data.items) { if (item.is_spam) continue; const chain = (byChain[item.chain_name] ??= { usd: 0, tokens: [] }); chain.usd += item.quote ?? 0; chain.tokens.push(item.contract_ticker_symbol); } return byChain;} const holdings = await zkRollupHoldings("0xd8dA6BF26964aF9D7eEd9e03E53415D37aA96045");for (const [chain, { usd, tokens }] of Object.entries(holdings)) { console.log(`${chain}: $${usd.toFixed(2)} in ${tokens.join(", ")}`);}Each item carries its chain_name, so the same code works whichever rollups you list. The address must be a hex address (ENS names aren't accepted on this endpoint). The GoldRush Foundational API covers the rest of the data an app needs per chain, such as transactions, token holders and NFTs, and the supported chains list shows which rollups each endpoint covers.
How to compare layer 2s
The choice between rollups is less about ZK vs optimistic than about the specific chain. The measures worth comparing:
- Throughput: transactions (or user operations) per second the chain actually processes, not its theoretical maximum.
- Fees: what a typical transfer or swap costs, which depends mostly on how the rollup pays for data availability.
- Time to finality: how long until a transaction is final on Ethereum, and how long a withdrawal to L1 takes.
- Value secured: the assets bridged to or issued on the chain (often reported as TVL).
- Decentralization and risk: who runs the sequencer and prover, whether users can force transactions and exit if the operator stops, where the data lives, and who can upgrade the contracts and how quickly.
These figures change weekly, so check them live rather than trusting a table in an article. ETHBEAT (formerly L2BEAT) tracks activity, value secured, data availability and risk for each L2, and its Stages framework rates how far each rollup has removed its training wheels.
Frequently asked questions
What is a ZK rollup?
A ZK rollup is a layer 2 blockchain that executes transactions off Ethereum and posts the transaction data and a new state root to Ethereum with a validity proof. A verifier contract on Ethereum checks the proof before accepting the new state, so the rollup inherits Ethereum's security without Ethereum re-executing its transactions.
How do ZK rollups work?
A sequencer orders and executes users' transactions and seals them into a batch. The batch's data and new state root are posted to Ethereum, a prover generates a validity proof that the state transition is correct, and a verifier contract on Ethereum checks that proof. Once the proof is verified, the batch is final and withdrawals in it can be completed on Ethereum.
What is the difference between ZK rollups and optimistic rollups?
ZK rollups prove every batch valid with a validity proof checked on Ethereum, so withdrawals can complete once the batch is proven. Optimistic rollups assume batches are valid and give anyone a challenge window, typically about seven days, to submit a fraud proof, so native withdrawals wait for that window. Arbitrum One, OP Mainnet and Base are optimistic; zkSync Era, Starknet, Linea, Scroll and Taiko are ZK rollups.
What is a zkEVM?
A zkEVM is a ZK rollup that can run Ethereum smart contracts. zkEVMs are grouped into types 1 to 4, from fully Ethereum-equivalent (Type 1, slowest to prove) to compiling Solidity to a different, proof-friendly VM (Type 4, fastest to prove but least compatible at the bytecode level).
What is the difference between a ZK rollup and a validium?
Both use validity proofs. A ZK rollup posts its transaction data to Ethereum, so anyone can rebuild the state and exit; a validium keeps the data off Ethereum with a data availability committee or an external data availability layer. A validium is cheaper, but if the data is withheld, users' funds can be frozen even though the state is proven correct.
Are ZK rollups private?
Not by default. Most ZK rollups publish all their transaction data, and use zero-knowledge proofs for succinctness, so that Ethereum can verify a large batch cheaply. Privacy-focused rollups such as Aztec use the zero-knowledge property to hide transaction details as well.
Next steps
- What is a modular blockchain?: execution, settlement, consensus and data availability layers, and where rollups fit.
- Mastering PeerDAS: how Ethereum scales blob data availability for rollups.
- Multichain balances reference: every parameter and response field for the GoldRush call above.
- Supported chains: the rollups and L1s GoldRush indexes.
- ZK rollups on ethereum.org: the protocol-level reference, with optimistic rollups and validiums alongside.